

Cybersecurity is becoming one of the most important skills in the digital world. Businesses, governments, startups, and individuals depend on technology every day. At the same time, cybercriminals are finding new ways to steal data, attack systems, and misuse artificial intelligence. This creates a growing need for people who can protect digital information and keep online systems safe.
But which cybersecurity skills will actually matter over the next five years? Should you learn ethical hacking, cloud security, artificial intelligence, or security automation? If you are a student, beginner, IT professional, or someone planning a career change, choosing the right skills can save you time and effort.
In this guide, I will explain the cybersecurity skills I would bet my career on between 2026 and 2031. You will learn what each skill means, why it matters, how to start learning it, and how to build practical experience without spending a fortune.
1. Why Cybersecurity Skills Will Matter Over the Next Five Years
Cybersecurity is about protecting computers, networks, applications, and data from digital attacks. Every company that uses technology needs some level of protection, whether it operates a small online store or a large financial institution.
The nature of these threats is changing. Artificial intelligence can help security teams find suspicious activity, but attackers can also use it to create convincing scams, automate attacks, and discover weaknesses. Cloud computing, connected devices, and remote work create additional areas that need protection.
A 2026 report from India’s Data Security Council of India highlights AI security, cloud security, governance, and cybersecurity architecture as important skill areas. It also identifies practical, hands-on ability as a major challenge for employers. Data Security Council of India+1
This is why I would focus on skills that help solve real security problems instead of learning only the names of tools.
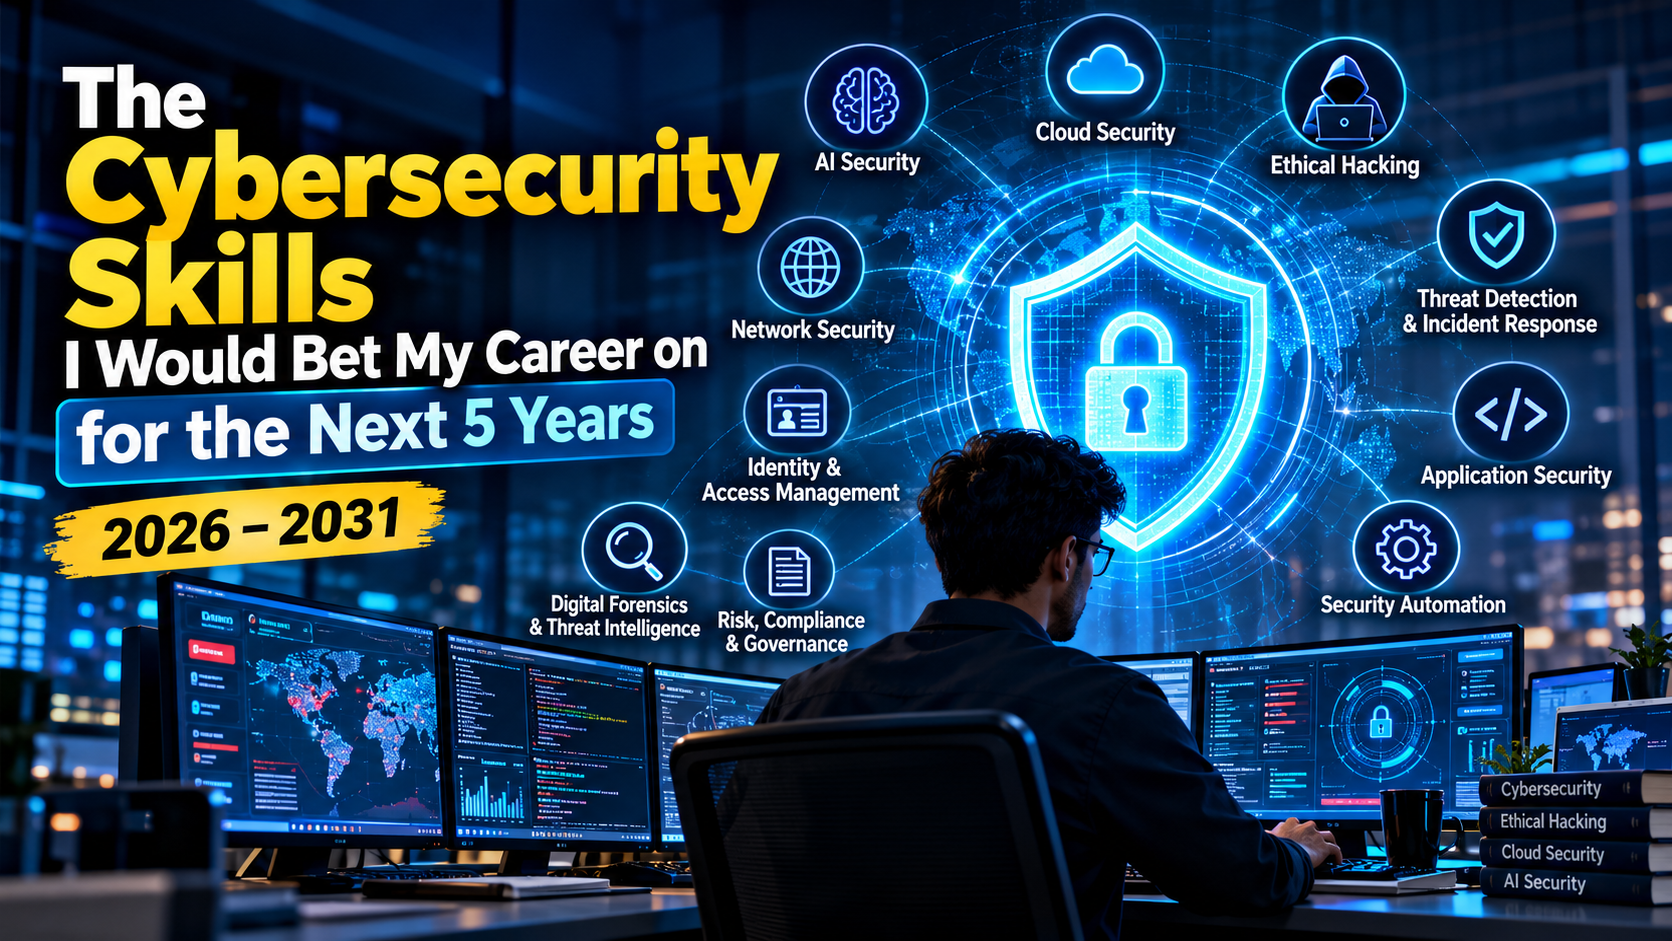
Here are the areas I believe are worth prioritising between 2026 and 2031:
- Artificial intelligence and AI security.
- Cloud security and infrastructure protection.
- Network security and operating systems.
- Ethical hacking and penetration testing.
- Security monitoring and incident response.
- Application security and secure coding.
- Identity and access management.
- Security automation and scripting.
- Digital forensics and threat intelligence.
- Communication, risk management, and security governance.
No one needs to master all these skills at once. The best approach is to build strong foundations, select a specialisation, and keep learning as technology changes.
2. AI Security and Artificial Intelligence Fundamentals
Training AI Without Data? Reverse-Approach Privacy Tech Draws Attention – Seoul Economic Daily
Artificial intelligence is one of the first cybersecurity skills I would invest time in. AI is changing how companies develop software, manage information, and protect their systems.
Security professionals need to understand both sides of this change: how AI can improve security and how AI systems themselves can become targets.
Why AI security matters
AI-powered security tools can analyse large amounts of information, identify unusual behaviour, and help analysts investigate potential attacks. However, AI systems can also produce incorrect answers, expose sensitive information, or be manipulated through specially designed inputs.
For example, a company may use an AI assistant to search internal documents. If that assistant has weak access controls, it could reveal information to someone who should not see it.
Security professionals must understand these risks before organisations can safely depend on AI.
What should you learn?
Start with the basic concepts of artificial intelligence and machine learning. You do not need to become an AI researcher to work in cybersecurity.
Focus on these skills:
- Understanding how large language models and AI assistants work.
- Recognising AI-generated phishing messages and other social engineering attempts.
- Learning about prompt injection and unsafe AI tool access.
- Understanding data privacy and sensitive information exposure.
- Testing AI applications for security weaknesses in authorised environments.
- Using AI tools to support threat analysis while checking their results.
- Learning the basics of AI governance and risk assessment.
You should also understand that an AI-generated security alert is not automatically correct. Human judgement remains important.
How can you practise?
Build a small AI application using sample or non-sensitive data. Test whether it follows access rules, handles unexpected inputs, and avoids exposing private information. Document the weaknesses and suggest fixes.
Career opportunities: AI security analyst, AI security engineer, application security specialist, and AI governance specialist.
AI security is a promising specialisation, but it is best combined with strong knowledge of traditional cybersecurity principles.
3. Cloud Security
AI linked to 83% of security breaches, Gigamon says
Cloud computing allows companies to store data, run applications, and manage services using platforms such as Amazon Web Services (AWS), Microsoft Azure, and Google Cloud.
Businesses value cloud technology because it can make their systems easier to scale and manage. However, cloud environments introduce security challenges involving permissions, data storage, network configuration, and account protection.
That is why cloud security is another skill I would bet on for the next five years.
Why cloud security is important
Imagine a business storing customer information in a cloud database. If the database is accidentally made public, sensitive information could be exposed without an attacker needing to break through a complicated security system.
Other risks include stolen cloud credentials, excessive permissions, insecure application interfaces, and poorly configured storage.
Cloud security professionals help prevent these problems through secure design, monitoring, and regular reviews.
What should you learn?
Start with one cloud platform instead of trying to learn all three at the same time.
Learn the following concepts:
- Cloud infrastructure and networking.
- Identity and access management.
- Multi-factor authentication.
- Secure storage and database configuration.
- Encryption and key management.
- Cloud logging and security monitoring.
- Backup and recovery.
- Cloud security posture management.
- Shared responsibility between the cloud provider and customer.
The shared responsibility model is especially important. A provider may secure the underlying cloud infrastructure, but customers still need to protect their accounts, data, permissions, and workloads according to the service they use.
How can you practise?
Create a free-tier or local learning environment, following the provider’s current pricing and usage limits. Configure a sample application with restricted permissions, enable logging, and review security settings.
You can also practise with infrastructure configuration examples and learn how to identify insecure permissions before deployment.
Career opportunities: Cloud security engineer, cloud security analyst, security architect, and cloud compliance specialist.
Cloud security is particularly valuable when combined with networking, identity management, and automation.
4. Networking and Operating System Fundamentals
Before learning advanced cybersecurity, you should understand how computers communicate and how operating systems work.
These fundamentals may seem less exciting than AI or ethical hacking, but they are essential for understanding how attacks happen and how to stop them.
Why networking matters
A network connects computers, servers, phones, applications, and other devices. Attackers may try to intercept traffic, access exposed services, misuse network protocols, or move from one compromised system to another.
Without networking knowledge, it is difficult to understand what a security alert actually means.
What should you learn?
Focus on the following concepts:
- IP addresses and subnetting.
- TCP and UDP.
- DNS and DHCP.
- HTTP and HTTPS.
- Firewalls and network segmentation.
- VPNs and secure remote access.
- Routers, switches, and ports.
- Basic packet analysis.
- Linux and Windows administration.
- Processes, permissions, users, and system logs.
Linux is especially useful because many security tools and servers use it. Windows administration is also important because many organisations depend on Windows systems and enterprise identity services.
How can you practise?
Install a Linux virtual machine and learn to use the terminal. Practise checking network connections, reviewing system logs, managing permissions, and identifying running processes.
Use Wireshark to examine network traffic from your own lab or other authorised sources. Learn to recognise normal activity before trying to identify suspicious behaviour.
Career opportunities: Security analyst, network security engineer, system administrator, and security operations centre (SOC) analyst.
My advice is simple: do not skip networking and operating system fundamentals just because you want to become an ethical hacker quickly.
5. Ethical Hacking and Penetration Testing
Pentesting en aplicaciones web paso a paso: Guía completa 2026
Ethical hacking involves testing systems with permission to discover security weaknesses before criminals can exploit them.
Penetration testing is a structured form of security testing in which an authorised professional attempts to demonstrate how weaknesses could be exploited and what impact they might have.
This field attracts beginners because it combines technical investigation, problem-solving, and practical experiments.
Why ethical hacking will remain relevant
Software is frequently updated, networks become more complex, and new weaknesses appear as systems change. Organisations need ways to test their defences and verify that important vulnerabilities have been fixed.
Automated tools can identify many common problems, but professionals still need to understand the results, determine real-world impact, and explain how to fix the issues.
What should you learn?
Build your knowledge in this order:
- Networking and Linux fundamentals.
- Common web application vulnerabilities.
- Authentication and session management.
- Input validation and access control.
- Basic scripting with Python.
- Vulnerability assessment and reporting.
- Manual testing and verification.
- Risk prioritisation and remediation.
The OWASP Top 10 is a useful starting point for understanding common web application security risks.
How can you practise?
Use intentionally vulnerable training applications such as OWASP Juice Shop or legal penetration-testing labs. Practise finding a weakness, documenting its impact, and explaining a safe fix.
Every test must remain within the scope of explicit authorisation. Never test a real website, server, or network just because it appears vulnerable.
Career opportunities: Penetration tester, ethical hacker, application security tester, and vulnerability assessment analyst.
Ethical hacking can be a rewarding career, but employers value reliable findings, clear reports, and responsible testing—not just the ability to run hacking tools.
6. Security Monitoring and Incident Response
Security monitoring is the process of watching systems for suspicious activity. Incident response is the process of investigating and managing a security incident.
I would treat these as core career skills because even organisations with strong preventive controls can experience security incidents.
Why these skills matter
A company might detect an unusual login, malware infection, suspicious data transfer, or compromised employee account. The security team must decide whether the activity is malicious and what action to take.
Poor decisions can allow an attacker to remain in the environment. A well-managed response can limit damage and help the organisation recover faster.
The 2026 UK cyber labour-market report identifies incident response among the important skills requested in cybersecurity job postings. GOV.UK+1
What should you learn?
Important skills include:
- Security Information and Event Management (SIEM) tools.
- Log collection and analysis.
- Alert triage and investigation.
- Endpoint detection and response.
- Basic malware behaviour.
- Incident classification and escalation.
- Containment, eradication, and recovery.
- Evidence preservation and incident reporting.
- Lessons learned after an incident.
You should also learn how to distinguish a genuine attack from harmless activity. Not every unusual event is a security incident.
How can you practise?
Create a small lab and generate sample system logs. Learn to search those logs for failed logins, unexpected processes, and unusual network activity.
Use sample security datasets to investigate a simulated incident. Write down what happened, what evidence supports your conclusion, and what steps you would recommend.
Career opportunities: SOC analyst, incident responder, detection engineer, and security operations engineer.
For beginners who enjoy investigation and problem-solving, a SOC analyst role can be a useful entry point into the cybersecurity industry.
7. Application Security and Secure Coding
Modern businesses depend on websites, mobile applications, APIs, and internal software. A vulnerability in one of these systems can expose sensitive data or allow unauthorised actions.
Application security focuses on finding and preventing these weaknesses throughout the software development process.
Why application security matters
Consider an online shopping application. If its access controls are poorly designed, a user might be able to view another customer’s order. If the application handles input incorrectly, an attacker might exploit a vulnerability to access information or interfere with the service.
Security testing should happen before and after software is released.
What should you learn?
Start with one programming language. Python is useful for automation and security scripts, while JavaScript is helpful for understanding web applications. Learning a language used by your target industry is also valuable.
Then study:
- Secure coding principles.
- Input validation and output encoding.
- Authentication and authorisation.
- API security.
- Database security.
- Dependency and package risks.
- Secrets management.
- Code review.
- Software composition analysis.
- Static and dynamic application security testing.
You do not need to become an expert programmer before learning security. However, the ability to read code and understand how applications work will make you much more effective.
How can you practise?
Build a small login system or sample web application. Review how it handles passwords, sessions, user permissions, and database queries.
Then test it in a local environment and improve the design. Keep notes showing the original problem, the fix, and the result.
Career opportunities: Application security engineer, product security engineer, secure software developer, and DevSecOps engineer.
Application security is a strong choice for people who enjoy both software development and cybersecurity.
8. Identity and Access Management
Identity and Access Management (IAM) controls who can access a system, what they can do, and how their access is managed.
This skill is especially important because attackers often try to misuse legitimate accounts instead of breaking through technical defences directly.
Why IAM will remain important
A stolen password can give an attacker access to email, business applications, cloud services, or confidential files. Excessive permissions can make the problem much worse.
Strong identity security reduces these risks by ensuring that users receive appropriate access and that suspicious activity can be detected.
What should you learn?
Focus on:
- Multi-factor authentication.
- Role-based access control.
- Least-privilege principles.
- Single sign-on.
- Identity lifecycle management.
- Privileged access management.
- Authentication logs.
- Account recovery security.
- Service accounts and application identities.
You should understand the difference between authentication, which verifies identity, and authorisation, which determines what an authenticated user can do.
How can you practise?
Create sample user accounts in a test environment. Assign different roles, restrict permissions, enable multi-factor authentication, and check whether each account can access only the resources it needs.
Also practise reviewing access logs and removing permissions that are no longer required.
Career opportunities: IAM engineer, identity security analyst, access management specialist, and cloud security engineer.
IAM is a useful specialisation because it connects cloud security, enterprise IT, compliance, and everyday business operations.
9. Security Automation and Python Scripting
Security teams often deal with large volumes of alerts, logs, vulnerabilities, and repetitive tasks. Automation helps them complete routine work more consistently and spend more time on difficult investigations.
Python is a practical starting point because it is widely used for scripting, data processing, and security-related tasks.
Why automation is worth learning
Imagine receiving hundreds of security alerts every day. A carefully designed script might help organise the alerts, remove duplicates, enrich records with useful information, or create a report.
Automation does not eliminate the need for security professionals. It makes their work more efficient, provided the scripts are tested and their actions are controlled.
What should you learn?
Start with:
- Python fundamentals.
- Variables, loops, functions, and error handling.
- Reading CSV, JSON, and log files.
- Working with APIs.
- Regular expressions.
- Basic data analysis.
- Git and version control.
- Workflow automation.
- Testing and documenting scripts.
- Safe handling of credentials and sensitive data.
After learning the basics, explore security orchestration, automation, and response (SOAR) platforms and workflow tools.
How can you practise?
Build a script that reads a sample log file, identifies repeated failed login events, and creates a summary report.
Later, create a small workflow that processes sample alerts and assigns priority levels based on predefined rules. Review the results manually before using any automated action that could affect a real system.
Career opportunities: Security automation engineer, detection engineer, security analyst, and SOAR engineer.
The strongest combination is cybersecurity knowledge plus the ability to automate repetitive work safely.
10. Digital Forensics and Threat Intelligence
Digital forensics and threat intelligence are two related skills that help organisations understand cyberattacks.
Digital forensics focuses on examining digital evidence to understand what happened on a device or system. Threat intelligence focuses on collecting and analysing information about attackers, their methods, and potential threats.
Why these skills matter
When a company experiences a security incident, it needs answers to important questions. Which account was compromised? What files were accessed? How did the attacker enter the system? Is the threat still active?
Digital forensics helps investigators build a timeline of events. Threat intelligence helps security teams understand attack patterns and improve their defences.
These skills can also help organisations identify threats before they cause significant damage.
What should you learn?
Start with the following concepts:
- Windows and Linux system artefacts.
- System and application logs.
- File metadata and timestamps.
- Basic memory and disk forensics.
- Evidence preservation.
- Incident timelines.
- Malware behaviour analysis.
- Indicators of compromise.
- Threat actor tactics and techniques.
- Threat intelligence reporting.
You should learn to distinguish facts from assumptions. A suspicious file does not automatically prove that a system has been compromised.
How can you practise?
Use publicly available training datasets and simulated incidents. Examine sample logs, identify suspicious events, and create a timeline showing how the incident developed.
You can also study the MITRE ATT&CK knowledge base to understand how attackers operate and how defenders can detect their techniques.
Career opportunities: Digital forensics analyst, threat intelligence analyst, incident investigator, and malware analyst.
This field is particularly suitable for people who enjoy detailed investigation, research, and evidence-based problem-solving.
11. Vulnerability Management and Risk Assessment
Vulnerability management is the process of identifying, assessing, prioritising, and fixing weaknesses in systems.
Many beginners assume that cybersecurity is mainly about finding vulnerabilities. In professional environments, deciding which weaknesses should be fixed first is just as important.
Why vulnerability management matters
A business may have hundreds of reported vulnerabilities. Its security team cannot always fix everything immediately because time, money, and operational requirements are limited.
The team must identify which vulnerabilities present the greatest risk to the organisation.
For example, a critical weakness in an internet-facing business application may require immediate attention, while a lower-risk issue on an isolated test system may be handled later.
What should you learn?
Build skills in:
- Asset inventory and discovery.
- Vulnerability scanning.
- Understanding CVE identifiers.
- Interpreting CVSS severity scores.
- Exposure and exploitability assessment.
- Patch management.
- Risk prioritisation.
- Remediation tracking.
- Verification and reporting.
Remember that a severity score is not the same as a complete business risk assessment. Exposure, existing controls, the value of the affected asset, and the potential impact also matter.
How can you practise?
Use a legal lab or a machine you own. Run an appropriate vulnerability scanner, review the results, and create a remediation plan.
Record which issues should be addressed first and explain why. After applying fixes, test the system again to confirm that the problems have been resolved.
Career opportunities: Vulnerability management analyst, security assessor, security consultant, and penetration tester.
This skill is useful across many cybersecurity roles because almost every organisation needs to manage technical risk.
12. Security Governance, Risk, and Compliance
Not every cybersecurity job involves writing code or testing networks. Some professionals focus on policies, regulations, risk management, audits, and security controls.
This area is often called Governance, Risk, and Compliance (GRC).
Why GRC will remain important
Organisations need to protect customer information, manage suppliers, meet legal requirements, and demonstrate that they follow appropriate security practices.
A company may have excellent technical tools but still face serious problems if employees do not follow secure processes or management does not understand its risks.
The 2026 UK cyber labour-market report lists governance, auditing, and risk management among frequently requested skills in core cybersecurity job postings. GOV.UK+1
What should you learn?
Focus on:
- Information security policies.
- Risk assessments.
- Security audits.
- Access control reviews.
- Incident response planning.
- Vendor and third-party risk.
- Data protection principles.
- Business continuity and disaster recovery.
- ISO/IEC 27001 fundamentals.
- NIST Cybersecurity Framework fundamentals.
You should also learn how to explain technical risks in plain language so that managers can make informed decisions.
How can you practise?
Choose a fictional small business and prepare a basic security risk assessment. Identify its important assets, possible threats, weaknesses, and potential consequences.
Then recommend practical controls, such as multi-factor authentication, backups, employee training, and access reviews.
Career opportunities: GRC analyst, information security auditor, risk analyst, security consultant, and compliance specialist.
GRC is an excellent path for people who enjoy planning, communication, documentation, and business problem-solving.
13. Zero Trust and Modern Security Architecture
Zero Trust is a security approach based on the principle that access should not be trusted automatically simply because a user or device is inside a company’s network.
Instead, access decisions should consider identity, permissions, device condition, context, and risk.
Why Zero Trust matters
Employees now work from offices, homes, mobile devices, and cloud applications. Traditional security models that rely heavily on a protected internal network are not enough on their own.
Zero Trust encourages organisations to verify access requests and limit the damage that can occur when one account or device is compromised.
What should you learn?
Important concepts include:
- Identity-based access controls.
- Least privilege.
- Device security.
- Network segmentation.
- Continuous monitoring.
- Strong authentication.
- Application-level access policies.
- Secure remote access.
- Security architecture design.
Zero Trust is not a single product. It is a broader strategy that combines multiple technologies, policies, and monitoring processes.
How can you practise?
Design a simple security architecture for a fictional company with remote employees and cloud applications. Show how users authenticate, how permissions are assigned, and how access is monitored.
Explain what happens if an employee’s device is compromised and how segmentation and restricted permissions could limit the impact.
Career opportunities: Security architect, enterprise security engineer, identity security specialist, and cloud security architect.
This is a longer-term skill that becomes more useful as you gain experience with networks, identity systems, cloud platforms, and security operations.
14. Communication and Problem-Solving Skills
Technical knowledge is important, but it is not enough by itself. Cybersecurity professionals must communicate clearly, investigate problems carefully, and work with people across an organisation.
A security analyst may discover a serious weakness, but the finding has limited value if nobody understands the risk or knows what action to take.
Which soft skills should you develop?
Pay attention to these areas:
- Clear communication: Explain technical problems in simple language.
- Critical thinking: Check evidence instead of making assumptions.
- Attention to detail: Notice small changes that may indicate a security problem.
- Documentation: Record investigations, findings, and recommendations.
- Teamwork: Coordinate with developers, IT staff, managers, and other analysts.
- Time management: Prioritise tasks according to risk and urgency.
- Ethical judgement: Protect privacy and follow authorised procedures.
How can you improve these skills?
After every practice project, write a short report describing the problem, the evidence, the potential impact, and the recommended fix.
Try explaining the same issue in two ways: one for a technical colleague and another for a business manager.
This simple habit can make your portfolio more useful and prepare you for real workplace responsibilities.
15. Which Cybersecurity Skills Should Beginners Learn First?
If you are starting from zero, learning every skill in this article at once will probably lead to confusion. A structured approach is more effective.
Here is the order I would recommend for a beginner.
Stage 1: Build your foundations
Months 1–2
Learn networking, Linux, Windows fundamentals, basic security concepts, and common cyber threats.
Stage 2: Practise technical skills
Months 3–4
Study Python basics, log analysis, web security, access controls, and security tools in legal lab environments.
Stage 3: Choose a specialisation
Months 5–6
Explore SOC analysis, penetration testing, cloud security, application security, or GRC.
Stage 4: Build a portfolio
Months 7–9 and beyond
Complete practical projects, document your results, prepare for relevant certifications, and apply for internships or entry-level positions.
This is an illustrative learning schedule, not a guarantee of job readiness. Your progress will depend on your existing knowledge, available time, and practice.
Free and useful resources
You do not need to spend a lot of money to begin learning cybersecurity. Start with reputable documentation and practical training resources.
- Cisco Networking Academy — networking and introductory cybersecurity learning.
- TryHackMe — guided cybersecurity labs and learning paths.
- Hack The Box — hands-on security challenges and practical labs.
- OWASP — web application security guides and learning resources.
- MITRE ATT&CK — a knowledge base of adversary tactics and techniques.
- NIST NICE Framework — information about cybersecurity work roles and the knowledge and skills they require.
Check each provider’s current free and paid options before choosing a course.
16. How to Build a Cybersecurity Portfolio That Employers Can Understand
A portfolio helps you demonstrate what you can do instead of relying only on a list of courses or certificates.
It does not need to contain advanced research. A few well-documented projects can show that you understand security concepts and can apply them to real problems.
Consider creating projects such as these:
- Network analysis project: Examine sample network traffic and explain unusual activity.
- Log monitoring project: Analyse sample logs and identify repeated failed login attempts.
- Vulnerability assessment: Scan a lab system, prioritise findings, and document fixes.
- Cloud security project: Configure a test environment with restricted permissions and appropriate logging.
- Python automation project: Create a script that processes sample security events.
- Incident response report: Investigate a simulated incident and write a clear timeline.
- Web application security project: Find and fix a weakness in an intentionally vulnerable application.
For each project, describe the objective, tools used, process, findings, limitations, and lessons learned.
Never publish real passwords, private keys, customer information, or confidential company data. Make sure your testing is authorised and your examples do not expose other people’s systems.
17. Cybersecurity Certifications: Are They Worth It?
Certifications can help you organise your learning and demonstrate knowledge to employers. However, a certificate alone does not guarantee employment or prove that you can handle a real incident.
The right certification depends on your experience and the job you want.
| Career stage | Possible learning or certification path |
|---|---|
| Beginner | CompTIA Security+ study path or introductory cybersecurity courses |
| Networking foundation | Cisco networking courses and relevant networking certifications |
| SOC and security operations | Security+ and role-specific SIEM or incident response training |
| Ethical hacking | eJPT or other practical penetration-testing training |
| Cloud security | AWS, Microsoft Azure, or Google Cloud security learning paths |
| Experienced professional | Advanced role-specific certifications, such as CISSP, where eligibility requirements are met |
| GRC and auditing | ISO/IEC 27001-related training and relevant risk or audit qualifications |
Certification names, exam requirements, prices, and eligibility rules can change, so check the issuing organisation’s current information before enrolling.
My recommendation is to combine structured learning with practical projects. If your budget is limited, learn the fundamentals, practise in free labs, and choose a certification only when it supports a clear career goal.
18. What Cybersecurity Career Should You Choose?
Different cybersecurity roles require different combinations of skills. You do not need to become an expert in everything to build a successful career.
| Career path | Main skills to prioritise |
|---|---|
| SOC analyst | Networking, log analysis, SIEM, incident triage |
| Penetration tester | Networking, Linux, web security, testing methodology |
| Cloud security engineer | Cloud platforms, IAM, networking, automation |
| Application security engineer | Programming, APIs, secure coding, vulnerability testing |
| Incident responder | Investigation, endpoint security, evidence handling |
| Threat intelligence analyst | Research, threat analysis, reporting, MITRE ATT&CK |
| GRC analyst | Risk assessment, policies, audits, compliance |
| Security automation engineer | Python, APIs, security workflows, data analysis |
| Security architect | Systems design, identity, cloud, risk, security controls |
If you are unsure where to start, try a few introductory projects from different areas. Your interests will become clearer when you see which activities you enjoy and which problems you find rewarding to solve.
19. My Five-Year Cybersecurity Career Strategy for 2026–2031
If I were planning a cybersecurity career today, I would focus on a combination of durable fundamentals and emerging specialisations.
I would not bet everything on one tool, one certification, or one fashionable technology. Tools can change, but the ability to understand systems, assess risk, investigate problems, and communicate solutions remains useful.
My approach would be to build three layers of skills.
Layer 1: Fundamentals. Learn networking, operating systems, identity, security principles, and basic scripting. These skills support almost every technical cybersecurity role.
Layer 2: Practical specialisation. Choose one main direction, such as cloud security, security operations, penetration testing, or application security. Build projects that demonstrate real understanding.
Layer 3: Future-focused skills. Add AI security, automation, advanced cloud controls, or security architecture as your experience grows.
This approach is supported by current workforce research. India’s 2025–2026 cybersecurity skills report identifies AI and generative AI security, hands-on technical capability, and cross-domain knowledge as important areas for organisations. Data Security Council of India+1
I would also review job descriptions regularly to understand which skills employers are requesting in my chosen location and specialisation.
Most importantly, I would treat learning as an ongoing process. Spending a few focused hours each week building and documenting projects is more useful than collecting courses without applying what you learn.
20. Common Mistakes to Avoid When Learning Cybersecurity
Even motivated learners can waste time by following the wrong strategy. Avoiding a few common mistakes can make your learning journey more effective.
- Learning tools without understanding the basics: Learn what a tool does, what its results mean, and when it can be wrong.
- Collecting certifications without practical work: Combine courses with projects and lab exercises.
- Trying to learn every specialisation at once: Build your foundation, then focus on one main career direction.
- Ignoring communication: Practise writing clear findings and explaining technical risks.
- Expecting a job immediately: Hiring depends on experience, local demand, role requirements, and your demonstrated skills.
- Using AI without checking its answers: Verify commands, explanations, code, and security recommendations before relying on them.
- Testing systems without permission: Practise only in your own environments or explicitly authorised labs.
- Ignoring basic security habits: Use multi-factor authentication, protect credentials, and keep your learning systems updated.
Cybersecurity rewards patience, careful thinking, and consistent practice. You do not need to know everything on your first day. You need to keep improving and learn how to solve problems responsibly.
Conclusion: The Cybersecurity Skills I Would Bet My Career On
The cybersecurity skills I would prioritise for the next five years are AI security, cloud security, networking, ethical hacking, incident response, application security, identity management, and automation. I would also invest in communication, risk assessment, and security governance.
These areas offer different career paths, but they work best when built on strong technical foundations. AI may change how security teams operate, yet organisations will still need people who understand their systems, recognise risks, investigate incidents, and make sound decisions.
For beginners, my advice is to start with networking and operating systems, practise basic security tasks, and choose a specialisation that matches your interests. Build projects, document your findings, and use certifications to support your learning rather than replace practical experience.
You do not need to master every cybersecurity skill to build a successful career. You need to develop the right foundations, practise consistently, and stay willing to learn. That is the approach I would trust most when planning a cybersecurity career from 2026 to 2031.
AGI vs AI vs ASI: What Is the Difference
Frequently Asked Questions (FAQs)
1. Which cybersecurity skills will be most important over the next five years?
AI security, cloud security, identity and access management, incident response, application security, and security automation are strong areas to prioritise. Networking and operating system fundamentals remain essential for understanding how attacks happen and how to defend against them.
2. Is cybersecurity a good career choice for beginners in 2026?
Yes, cybersecurity can be a good career choice for beginners who enjoy technology, investigation, and problem-solving. However, entry-level positions can be competitive. Building practical skills, completing projects, and developing a strong understanding of IT fundamentals can improve your readiness for available roles.
3. Can I learn cybersecurity without a computer science degree?
Yes. You can learn cybersecurity through online courses, practical labs, documentation, and independent projects. Some employers require specific degrees or qualifications, but others place considerable value on technical ability, relevant experience, and certifications.
4. Which cybersecurity skill should I learn first?
Start with networking, Linux, Windows fundamentals, and basic security concepts. Once you understand how computers and networks work, move towards a specialisation such as security operations, ethical hacking, cloud security, or application security.
5. Is Python necessary for cybersecurity?
Python is not essential for every cybersecurity job, but it is a valuable skill. It helps you automate repetitive tasks, analyse logs, process security data, and work with APIs. Basic scripting can make you more effective in many technical roles.
6. Will artificial intelligence replace cybersecurity professionals?
AI will automate some repetitive tasks and change how security teams investigate threats. However, human judgement remains important for understanding business risks, verifying findings, responding to complex incidents, and making decisions. Learning to use AI safely can help professionals adapt to these changes.
7. Is ethical hacking still worth learning?
Yes. Ethical hacking teaches you how to identify weaknesses and test security controls with permission. It is a useful specialisation for people interested in penetration testing, vulnerability assessment, and application security. Practical knowledge and responsible testing are more valuable than simply knowing how to operate hacking tools.
8. Which cybersecurity certification should a beginner choose?
CompTIA Security+ is one option for learning broad security concepts. Beginners can also explore introductory courses before deciding whether to pursue a certification. Your choice should depend on your current knowledge, budget, and intended career path.
9. How long does it take to learn cybersecurity?
You can learn basic concepts within a few months of consistent study. Becoming ready for a particular job may take considerably longer, depending on your previous experience, study time, practical work, and the requirements of the role. There is no single timeline that guarantees employment.
10. What is the best cybersecurity career for the future?
There is no single best career for everyone. Cloud security, AI security, application security, security operations, and security architecture are worth exploring. The right choice depends on your interests, existing skills, and the opportunities available in your target market.
11. Can I learn cybersecurity for free?
Yes. You can begin with free networking resources, Linux documentation, OWASP guides, MITRE ATT&CK, and free or limited-access cybersecurity labs. Some advanced courses, exams, and platforms charge fees, so check their current terms before enrolling.
12. How can I get my first cybersecurity job without experience?
Build a portfolio with practical projects, learn the fundamentals, and apply for suitable internships and entry-level positions. Roles such as junior SOC analyst, IT support technician, and security trainee can be useful starting points. Tailor your CV to the role and clearly explain what you learned from each project.